N-able Cloud Platform Plunges Offline Amid Mass Vulnerability Disclosure
N-able takes its cloud platform offline following the public disclosure of more than 30 critical vulnerabilities, raising significant supply chain concerns for

In a decisive, albeit disruptive, move for its global client base, N-able, a prominent provider of IT management and monitoring solutions for Managed Service Providers (MSPs), has taken its cloud platform offline. This drastic measure follows the public disclosure of over 30 critical vulnerabilities, described by some as “zero-days,” within its systems.
The unscheduled shutdown, impacting MSPs worldwide who rely on N-able's suite of remote monitoring and management (RMM) tools, underscores the severity of the discovered flaws. While N-able has yet to release a comprehensive technical bulletin detailing each vulnerability, the sheer volume suggests a potential for widespread exploitation, ranging from remote code execution (RCE) to privilege escalation and unauthorized data access.
The Fallout: Systemic Risk for MSPs
N-able's offerings are foundational to the operational security and efficiency of countless MSPs, who in turn manage the IT infrastructure for a diverse array of businesses, from small and medium-sized enterprises to large corporations. A critical flaw in an RMM platform like N-able's presents a profound systemic risk. Attackers leveraging such vulnerabilities could gain unfettered access to not only the MSP’s internal networks but, more critically, to the entire client ecosystem they manage.
This incident echoes past supply chain compromises where vulnerabilities in widely used IT management tools led to cascading security breaches across thousands of downstream organizations. The proactive shutdown by N-able, while causing immediate operational headaches, is a necessary step to prevent active exploitation and allow for thorough remediation and patching. MSPs utilizing N-able are advised to monitor official communications closely, prepare for urgent patching cycles, and review their own internal security postures, including multi-factor authentication (MFA) enforcement and network segmentation.
The Global Angle: Supply Chain Implications
For the "ThreatSurface Global" audience, this N-able incident serves as a stark reminder of the pervasive and intricate nature of supply chain risks in modern cybersecurity. The global interconnectedness of IT infrastructure means a single point of failure or compromise in a critical vendor, especially one embedded deep within the operational fabric of MSPs, can ripple across continents.
Nation-state actors and sophisticated criminal enterprises frequently target MSPs as a strategic entry point to compromise their diverse client portfolios without needing to breach each target individually. While the origin of these disclosed vulnerabilities has not been attributed, the potential for malicious actors to weaponize them against a vast, global target set is undeniable. Organizations globally, whether direct N-able clients or managed by an N-able-dependent MSP, must consider this event a high-alert situation. It necessitates immediate verification of incident response plans, enhanced monitoring for anomalous activity originating from RMM tools, and proactive threat hunting efforts. This incident reinforces the need for every organization to understand their third-party risk exposure and implement robust defense-in-depth strategies, regardless of their service provider's security assurances.
Source: Google News · zero-day

Critical RMM Zero-Day Forces N-able Offline, Heightens Global Supply Chain Alarm
A critical zero-day vulnerability has forced N-able to take its N-central RMM platform offline. ThreatSurface Global examines the supply chain implications for

Automated Attack Compromises 1.5 Million Revolve Customer Payment Details
Online retailer Revolve confirms 1.5 million customer payment details compromised in a September breach. ThreatSurface Global investigates the automated attack

QNAP NAS Devices Under Siege: Plex2Shell Exploitation Surges, Urgent Action Required
QNAP NAS devices running Plex Media Server are targeted by widespread Plex2Shell exploits. ThreatSurface Global details the critical RCE vulnerability and…
Critical cPanel Zero-Day Lurked for Weeks, Threatening Global Web Infrastructure
A critical cPanel zero-day (CVE-2026-41940) was exploited for over 25 days, leaving global web infrastructure vulnerable. ThreatSurface Global examines the…
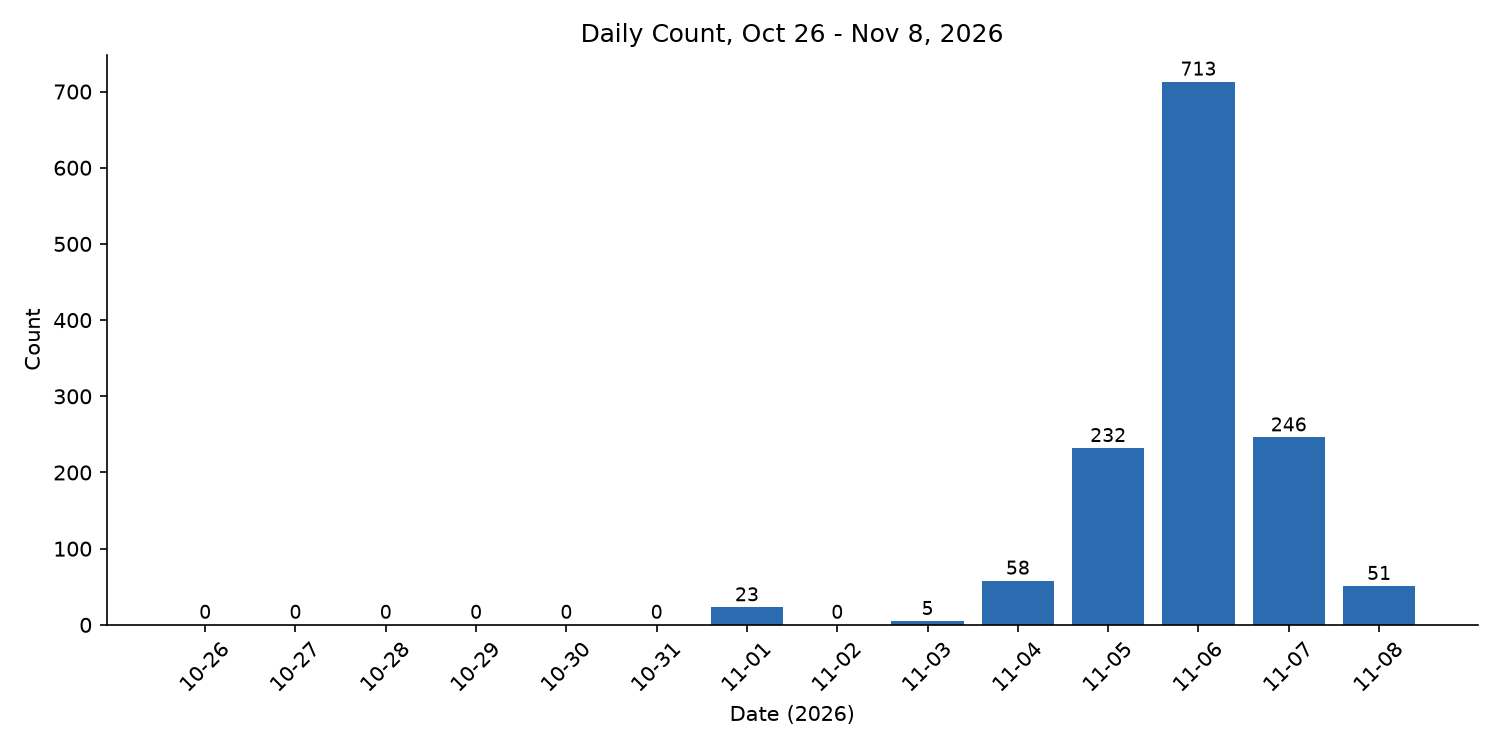
Sshole Vulnerability Triggers Global SSH Scan Surge: Exploitation Attempts Spike
New data reveals a global surge in exploitation attempts targeting CVE-2026-123158, the Sshole SSH vulnerability. Urgent patching and robust defenses…
BeyondTrust Zero-Day Exploited by Chinese APT: A Global Privilege Management Alert
A Chinese APT group exploited a zero-day in BeyondTrust Privilege Management for Windows, posing a global threat to privileged access. Learn about the exploit…
Network Edge Exposed: Critical Zero-Days Imperil D-Link Enterprise Switches
Urgent alert for D-Link Enterprise Gigabit Switch users. New critical zero-day vulnerabilities expose networks to severe threats. Act now to mitigate risks.